
Your AI-built app works. Until real users show up. I make it production-ready.
Lovable, Bolt, Replit and Cursor are great for building fast. But fast isn't the same as secure, scalable or maintainable. Before you launch or raise, I find what will break, starting with security, and turn your prototype into software you can grow on.
No pitch deck needed. Just bring your app link.

Wilmer Caceres
Senior Software Engineer
Things non-technical founders tell me
Sound familiar?
“Every time I ask the AI to fix one thing, it breaks two others.”
“I'm scared it's going to crash when more people start using it.”
“I have no idea if my users' data is actually safe.”
“An investor asked about my tech stack and I didn't know what to say.”
“Every developer I talk to says I need to rewrite everything.”
None of this means your app is bad. It means it was built to prove an idea — and now it needs to carry a business.
What's usually hiding in a vibe-coded app
Exposed keys and secrets
API keys and database credentials sitting in the frontend where anyone can find them.
Data anyone can read
Database rules (like missing Supabase row-level security) that let one user see (or delete) another user’s data.
Login that isn’t really secure
Authentication and permissions that look fine but can be bypassed.
Code that fights back
No structure and no tests, so every change risks breaking something else.
Costs that explode with growth
Inefficient queries and infrastructure that get expensive fast.
No warning when things fail
No monitoring, so you hear about bugs from angry users.
Three steps
How I fix AI-generated code
Step 1: Production Readiness Audit
$199 USD~5 days
I review security, architecture, database and costs — including a Supabase security review if that's your backend. You get a prioritized report: what's critical, what can wait, and a clear action plan. You keep the report whether or not you hire me for the next step.
Step 2: Rescue & Hardening
$1,400–$2,8003–6 weeks
I fix the vulnerabilities, set up real authentication and permissions, restructure the code, add tests, automated deployments and monitoring. The result: an app that can handle thousands of users — built on what you already have.
Step 3: Fractional CTO & Maintenance
$2,000/month
Ongoing technical partnership so you can keep shipping features without breaking everything again. Also useful when investors ask about your tech.
Not sure where to start?
Book a free 30-min app review(opens Calendly in a new tab)I don’t start by telling you to throw it away.
Most developers look at AI-generated code and say “rewrite it.” That costs months and money you may not have. My approach is to keep what works, fix what’s dangerous first, and improve the rest step by step — so your product keeps running while it gets stronger.
Results I’ve delivered in production.
2 weeks → 2 hours
Fully automated recurring billing for 1,000+ SaaS customers. I centralized the data source and eliminated 100% of manual billing errors.
Automated accounting integration
Designed, together with accounting experts, real-time sync with QuickBooks and Xero for a payroll platform. Used by 200+ companies, saving them hundreds of hours of manual data entry.
Code rescue, ready to scale
Refactored a critical system with a high error rate and serious technical risk. Cut reported bugs by 98%, improved response times and left the platform ready to scale to thousands of concurrent users.
Cloud costs cut by 76%
Audited the AWS architecture of an over-provisioned app, right-sized instances and simplified cloud services. Monthly costs dropped from $1,700 to $400.
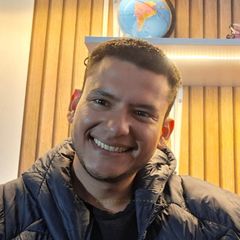
About me
I’m Wilmer, a Senior Software Engineer with 4+ years building SaaS products for U.S. companies. I work with Node.js, TypeScript, NestJS, Python (FastAPI), React/Next.js, PostgreSQL, AWS and Docker.
My background is in Clean and Hexagonal Architecture and testing, and I’m currently a Senior Full-Stack Developer for a U.S. company. I’m based in Colombia — same or close time zones as U.S. founders — and I work in fluent English (and Spanish).
Frequently asked questions
AI-built apps, security and Supabase
How secure are Lovable apps?
It depends less on Lovable than on how your app is configured. Lovable generates a solid front end, but security lives in the backend: database access rules, authentication, and where API keys are stored. The most common problem I see is Supabase tables without proper row-level security, which can let users read data that isn’t theirs. An audit checks exactly these points.
What are the security risks of apps built with AI?
The usual ones are API keys exposed in the browser, database rules that let users see each other’s data, login and permission checks that only happen in the front end, missing input validation, and outdated dependencies. AI tools optimize for “it works,” not “it’s safe,” so these gaps are easy to miss until someone looks for them on purpose.
Can my Lovable app be SOC 2 compliant?
SOC 2 isn’t something an app or a tool has on its own: it’s an audit of your company’s controls, done by an independent CPA firm. A Lovable-built app can be part of a SOC 2 program, but you’ll need access controls, logging, backups, change management and vendor reviews. I can help get the technical side ready; the audit itself is done by an auditor.
Where does my Lovable app store data?
Lovable apps typically use Supabase, a hosted PostgreSQL database, for data, user accounts and file storage. That’s either a Supabase project you connected and own, or Lovable Cloud, which runs on Supabase but is managed through Lovable. Your code can be synced to GitHub. Knowing which setup you have matters for backups, access control and who can reach your data.
Is Supabase secure enough for production?
Yes. Supabase is built on PostgreSQL and runs many production apps. The risk is usually configuration, not the platform: row-level security turned off or too permissive, the service role key exposed in the front end, public storage buckets, or no backups. Once those are reviewed and fixed, Supabase is a reasonable production backend for most early-stage products.
Can a Lovable app be published to the App Store?
Not directly. Lovable builds web apps, and the App Store expects a native app. The common route is wrapping the app with a tool like Capacitor and submitting it through an Apple Developer account. Apple may reject apps that are just a website in a wrapper, so it usually needs native touches like push notifications, offline handling and a mobile-first interface.
How do I migrate from Lovable Cloud to Supabase?
In broad strokes: connect your project to GitHub so you own the code, create your own Supabase project, apply the database schema, then move the data, storage files, edge functions and secrets, and point the app to the new keys. User accounts need extra care so nobody loses access. It’s very doable, but test it on a copy before switching real users over.
Does vibe coding actually work for real products?
For getting to a working product and your first users, yes. Many real businesses start that way. Where it struggles is what comes next: security, a data model that holds up as you grow, tests, monitoring and code another developer can maintain. That doesn’t mean starting over. It means hardening what you already have before it carries more users and money.
Working with me
Do I need to know how to code?
No. I explain everything in plain English and the audit report is written for founders, not engineers.
Will you make me rewrite my app?
Almost never. I keep what works and fix what’s risky first. If something truly needs rebuilding, I’ll explain why and what it costs before touching it.
Which tools do you work with?
Apps built with Lovable, Bolt, Replit, Cursor, v0 and similar — typically React/Next.js frontends with Supabase, Firebase or Node backends.
Is my code and data safe with you?
I’m happy to sign an NDA before seeing anything, and I only request the access needed for each step.
How long does it take?
The audit takes about 5 days. A full rescue usually takes 3 to 6 weeks depending on size.
What happens on the call?
30 minutes. You show me the app and tell me what worries you. I’ll tell you honestly whether I can help and what I’d look at first. No obligation.
You’re in Colombia — how does that work?
Fully remote, overlapping U.S. working hours, async updates plus scheduled calls.
Launch with confidence, not with fingers crossed.
Tell me about your app. In 30 minutes you’ll know what’s most likely to break and what to fix first.
Book a free 30-min app review(opens Calendly in a new tab)